
The Qualitative Impact of AI Phishing: Beyond Click Rates
Discover how AI phishing affects trust, security decisions, and reporting and which security culture metrics reveal the human risk that click rates miss.
A low phishing click rate does not necessarily mean low human risk. AI-enhanced phishing can influence how collaborators judge requests, verify identities, report suspicious activity, and trust legitimate communications—creating business risk even when no credentials are compromised.
Generative AI is making AI-driven phishing threats more contextual, personalized, and scalable. To assess AI phishing risks accurately, CISOs need to look beyond quantitative outcomes such as clicks, credential submissions, attachment openings, or reports.
The psychological impact of cyberattacks also appears in less visible signals: hesitation, misplaced trust, stress, verification behavior, reporting willingness, and confidence when making security-sensitive decisions.
This distinction matters because human risk is business risk. Probability alone does not determine risk; the potential impact on confidentiality, integrity, and availability also matters. Effective Human Risk Management therefore requires security culture metrics that reveal behavior and business impact—not click rates alone.
Why AI Phishing Has a Different Psychological Impact
AI phishing does not reinvent social engineering; it makes established psychological triggers harder to recognize. By producing more contextual, personalized, and credible messages in large volumes, AI can reduce familiar detection cues and increase the psychological impact of cyberattacks on everyday decision-making.
Hyper-personalization increases perceived legitimacy
Generative AI can reproduce organizational language, role-specific terminology, and plausible business requests. A fraudulent message that references a real project, supplier, or workflow creates less distance from normal communication.
This evolution toward AI-generated impersonation does not make deception infallible. It makes legitimacy harder to assess from superficial cues alone.
Authority, urgency, and familiarity become easier to reproduce
AI phishing risks increase when personalization reinforces established decision shortcuts: authority, urgency, familiarity, social proof, or reciprocity. An attacker can impersonate an executive requesting an urgent payment, a supplier changing account details, or a colleague asking for sensitive information.
The security consequence is not simply a higher probability of clicking. The attacker is attempting to manipulate the decision itself.
Cognitive load makes good judgment harder
Collaborators rarely evaluate suspicious messages in isolation. They do so between meetings, deadlines, notifications, and competing tasks.
NIST research on human-centered cybersecurity identifies cognitive overload, working-memory limitations, and time pressure as factors that can impair cybersecurity decision-making. This reinforces Kymatio's analysis of digital stress and cyber errors.
AI phishing susceptibility should therefore be treated as a contextual human-risk variable, not as an individual failure.
The Hidden Cost of AI Phishing: Erosion of Organizational Trust
The psychological impact of AI phishing can persist even when no breach occurs. Repeated exposure to credible deception can make collaborators distrust legitimate communications, hesitate before routine actions, or become desensitized to suspicious requests. The result can be operational friction as well as increased human risk.
When legitimate messages start to look suspicious
Healthy skepticism supports security. Generalized distrust does not. A collaborator who struggles to distinguish legitimate communications from AI-generated impersonation may delay an urgent approval, ignore an HR message, or create verification bottlenecks with suppliers.
The risk increases when AI-enabled fraud targets senior leaders because attackers can exploit familiar voices, organizational roles, and perceived authority.
Security fatigue and the “everything could be fake” problem
NIST research on security fatigue identified consequences including resignation, loss of control, risk minimization, and decision avoidance.
Security processes should encourage reliable verification without creating generalized suspicion. Persistent ambiguity, combined with digital stress and cyber errors, can increase security fatigue and undermine that balance.
The reporting paradox
A convincing lure creates another risk after the initial interaction: embarrassment or fear of blame may delay reporting.
Security culture metrics should therefore capture how quickly collaborators report potential mistakes, not simply whether they avoid them. A culture that makes early reporting safe gives security teams more time to contain an error before it develops into a business-impacting incident.
Why Click Rates Cannot Measure Security Culture
Why are phishing click rates not enough to measure security culture? Click rates measure a single observable action. Security culture metrics must also show whether collaborators recognize manipulation, verify unusual requests, report threats quickly, recover from mistakes, and change their behavior over time.
A click is an event, not a complete risk profile
Two collaborators can click the same lure yet represent very different levels of business risk. Consider a collaborator with limited access who clicks and immediately reports the message versus a finance executive who submits credentials and has authority to approve payments.
In practice, two identical simulation outcomes can represent very different levels of human risk when role, access, reporting behavior, and potential business impact are considered. A click may indicate the same probability event, but it does not represent the same business risk.
Vanity metrics can hide behavioral risk
Click rates, completion rates, and campaign pass/fail results are easy to communicate, but they can become vanity metrics when separated from how collaborators actually respond to threats.
This aligns with ENISA’s behavioral approach to cybersecurity culture, which draws on disciplines including psychology, sociology, and behavioral economics.
Measure trajectory, not isolated performance
Industry phishing benchmarks provide useful reference points for comparing click rates, but they cannot measure security culture or replace a contextual human-risk model.
Human-risk KPIs and dashboards should track changes in security decisions over time: Is reporting becoming faster? Are high-impact teams improving? Do the same manipulation techniques repeatedly succeed?
Effective security culture metrics reveal changes in decision-making and business exposure—not simply whether someone clicked.
Security Culture Metrics That Reveal AI Phishing Risk
The most useful security culture metrics show whether collaborators make safer decisions—not merely whether they avoid clicking. Combine reporting, verification, detection quality, and behavioral improvement to determine whether your organization is becoming more resilient to AI phishing risks.
1. Reporting behavior
Track phishing reporting rate and time-to-report, but also whether collaborators report before or after interacting with a suspicious message. False positives provide useful context too.
Fast reporting after a mistake should not automatically count as failure. Rapid escalation is itself a resilience behavior because it gives security teams an earlier opportunity to contain potential exposure.
2. Verification behavior
Measure whether collaborators independently verify unusual requests involving payments, credentials, sensitive data, or access privileges. Out-of-band verification—using a trusted channel rather than replying to the suspicious communication—is an especially valuable behavioral security metric and human risk indicator.
3. Detection quality
Do not reduce detection quality to “clicked/didn’t click.” Identify which manipulation cues collaborators recognize and which psychological triggers repeatedly succeed. This provides more actionable insight into the psychological impact of cyberattacks than an organization-wide average.
4. Recovery and behavioral improvement
ENISA guidance on cybersecurity awareness recommends measuring behavior regularly rather than treating awareness as a one-off activity.
Track whether collaborators make safer decisions after assessments, Attack Simulations, and targeted awareness actions, and whether those improvements persist over time. Segment trends by role or department when business impact justifies it.
A practical methodology for calculating human risk can then connect these signals with risk context, while simulation results can become evidence for NIS2 and ROSI. The objective is measurable behavioral change, not simply an improvement in campaign statistics.
From AI Phishing Metrics to NIS2 Human Risk Management
For organizations in scope of NIS2, measuring human behavior should inform cybersecurity risk-management decisions and provide evidence of ongoing oversight—not simply produce better campaign statistics. The objective is to turn AI phishing risks into measurable business risk that management can prioritize, mitigate, and review.
1. Measure: Translate behavior into business risk
A successful AI phishing lure against a collaborator with privileged access, payment authority, or sensitive data exposure can have more serious business consequences than the same response in a lower-risk role. Security culture metrics need business context alongside probability.
2. Prioritize: Turn simulations into evidence
Repeated assessments, Attack Simulations, targeted awareness actions, remediation, and trend monitoring create a traceable management process. Together, these records can support audit-ready NIS2 evidence and connect individual simulation results with continuous human risk monitoring and accountability.
3. Evidence: Make leadership part of the control environment
Articles 20 and 21 of the NIS2 Directive connect cybersecurity risk management with management-body approval and oversight. NIS2 does not prescribe a specific phishing KPI.
Behavioral evidence and security culture metrics can help demonstrate that human-related cybersecurity risks are identified, addressed, monitored, and reviewed. This matters because NIS2 makes cybersecurity governance a management responsibility, with direct implications for senior leadership.
Conclusion: Treat AI Phishing as Human Risk, Not a Click-Rate Problem
AI phishing risks make one measurement problem impossible to ignore: a campaign result is not a complete human-risk assessment. Organizations need to measure behavioral change and trust, interpret those signals according to business impact, and build a security culture where verification and rapid reporting are rewarded.
A reliable human-risk assessment therefore needs more than isolated metrics. Use meaningful human-risk KPIs and behavioral security metrics to identify patterns, vulnerable groups, and improvement over time.
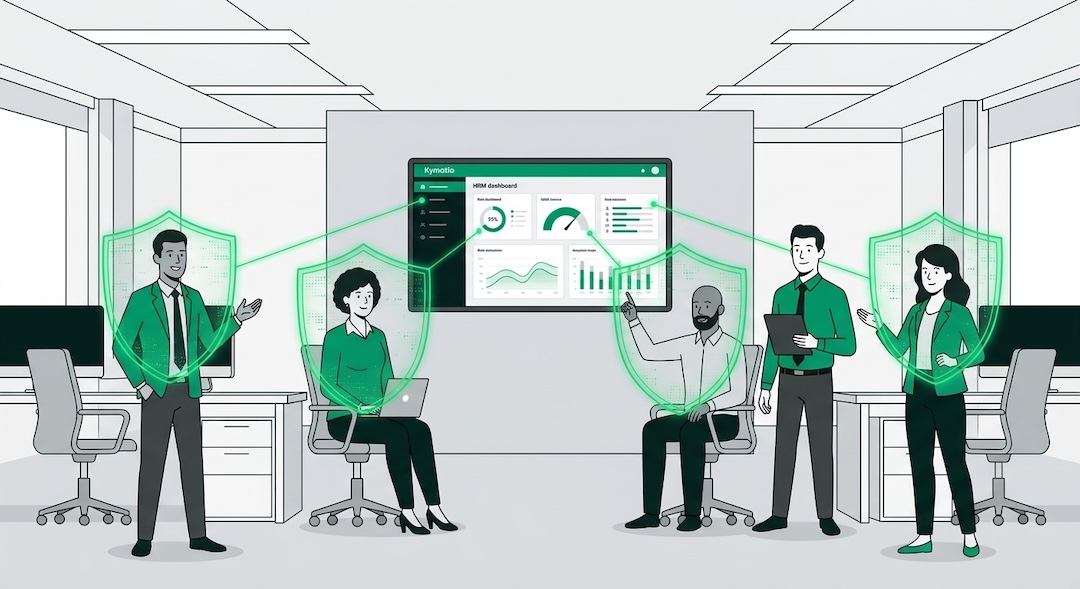
Kymatio's Human Risk Management approach combines continuous assessment, personalized awareness, exposed-credential monitoring, and Social Attack Simulations to proactively assess, measure, and mitigate human risk.
The objective is not simply fewer clicks. It is better security decisions and lower business risk. Explore how Human Risk Management addresses AI-accelerated threats.
Frequently Asked Questions


AI phishing can increase the credibility and personalization of social engineering. The risk extends beyond clicks to manipulated decisions, misplaced trust, delayed reporting, credential exposure, and changes in security behavior.
Credible deception can increase stress, uncertainty, distrust, and security fatigue. These effects can influence how collaborators verify requests, report incidents, communicate, and make security-sensitive decisions.
Measure reporting rates, time-to-report, verification behavior, detection quality, recovery after mistakes, behavioral trends, and role-specific business impact. Click rates remain useful, but only as one signal within a broader human-risk assessment.
CISOs should track reporting speed, verification behavior, detection quality, recurring behavioral patterns, departmental trends, and improvement after targeted awareness and Attack Simulations. Metrics should be interpreted according to business impact.
NIS2 requires organizations in scope to implement appropriate cybersecurity risk-management measures and establishes management oversight responsibilities. Human-risk evidence can help demonstrate that human-related risks are identified, addressed, monitored, and reviewed.
Combine probability indicators with behavioral evidence and business impact. Assess who is exposed, what access or authority they have, how they verify and report suspicious requests, and whether their behavior improves over time.

Join the Kymatio® newsletter and get the latest insights, research, and practical tips on cybersecurity awareness prevention straight to your inbox.
